Cybersecurity designed for corporate environments don't address the requirements of the healthcare industry, according to an article on the CSO website.
To avoid dealing with the aftermath of cyberattacks, healthcare providers should place digitized assets into categories, each with its own security protocols and protections.
Most assets in a healthcare setting can be deemed administrative systems, clinical information systems, or modalities – internet-connected clinical devices and systems for diagnosis and treatment.
Determining how each asset within a category can be accessed – by both legitimate users and criminals – can help ascertain the potential impact on an attack and the controls that may be appropriate to protect data integrity without compromising functionality and patient safety, the article said.
 Hospitals Are Energy Super-Users. Why Is It So Hard to Modernize Them?
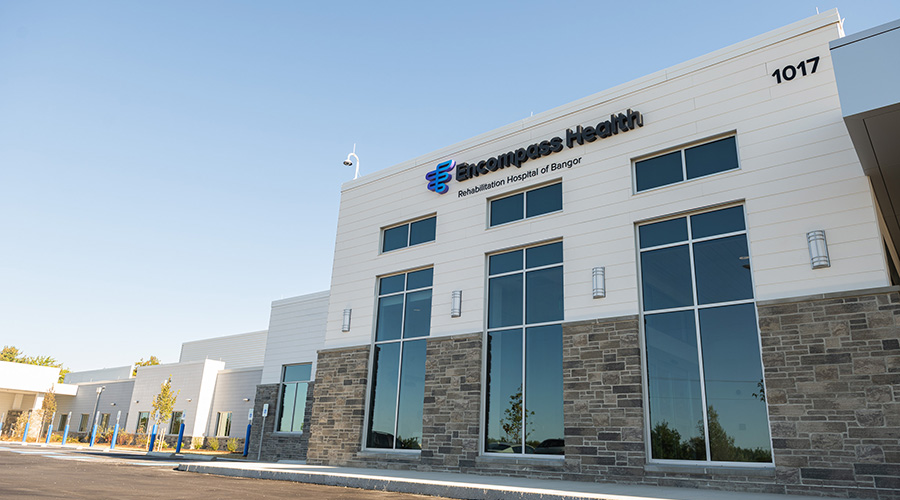 Encompass Health Rehabilitation Hospital of Bangor Officially Opens
 Early Entry: Manager's Critical Role in Construction Planning
 The Evolution of Lighting in Patient Care
 HealthPartners and Essentia Health to Combine Organizations