Naming a chief information security officer (CISO), maintaining a separate budget and stating a strategic objective are some of the crucial elements of a healthcare facility cybersecurity plan, according to an article on the Healthcare IT News website.
Board involvement and strict vendor scrutiny are also on the experts' must have list.
“Information risk management will inform many decisions that require organizational prioritization and ensure the C-suite and board are well-informed on threats, vulnerabilities and risks that may adversely impact the organization,” according to Rich Curtiss, a managing consultant at Clearwater Compliance.
Information security workforce should be from the information technology workforce to ensure adequate separation of duties and avoid conflicts of interest, Curtiss said.
 Building Around Care: Lessons in Modernizing Active Healthcare Environments
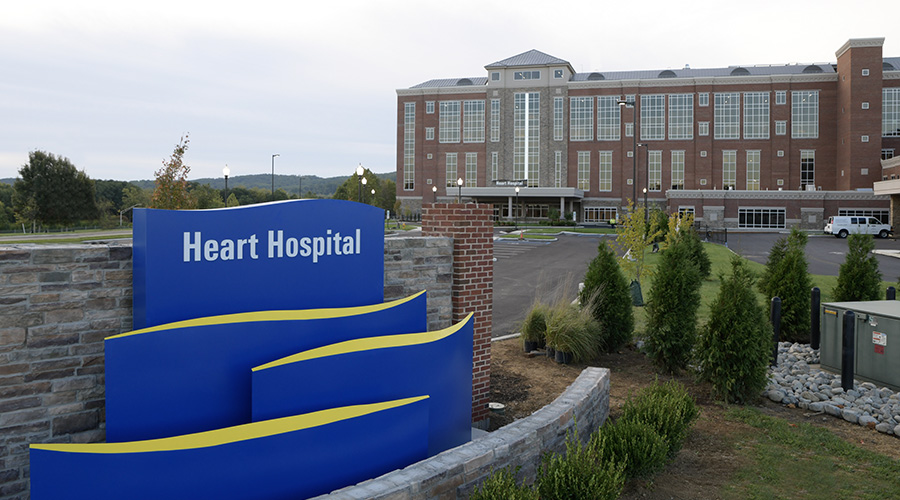 St. Luke's Heart Hospital Opens at Anderson Campus in Pennsylvania
 WindRose Health Network Ensnared in Vendor Data Breach
 How Efficiency Checklists Help Hospitals Save Energy, Water and Money
 Intermountain Healthcare Receives $50M Gift for Standalone Children's Hospital