The Department of Health and Human Services (HHS) has released a new fact sheet: Ransomware and HIPAA to address the risks of victimization, according to an article on the Healthcare IT Security website.
Organizations are already required by HIPAA to have a security management process in place. They should also have procedures in place against ransomware while training end users to detect and report potential ransomware issues, the article said.
Access to electronic patient information and software programs should be limited to those requiring specific access. A contingency plan should cover emergency operations, disaster recovery, frequent data backups and test restoration.
HIPAA compliance requires that all IT end users be trained on detecting and reporting security risks.
 Building Around Care: Lessons in Modernizing Active Healthcare Environments
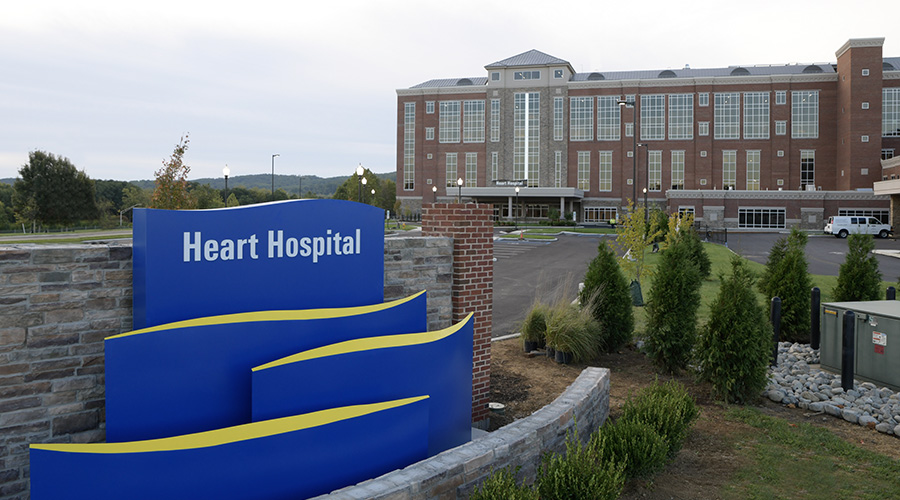 St. Luke's Heart Hospital Opens at Anderson Campus in Pennsylvania
 WindRose Health Network Ensnared in Vendor Data Breach
 How Efficiency Checklists Help Hospitals Save Energy, Water and Money
 Intermountain Healthcare Receives $50M Gift for Standalone Children's Hospital