Cybersecurity responsibility shared by entire healthcare supply chain

Increased use of connected medical devices and software and wireless technology have made health systems more vulnerable


The increased use of connected medical devices and software and wireless technology have made health systems more vulnerable, according to an article on the Med Tech Dive website.

The responsibility for the cybersecurity is shared by entire healthcare supply chain.

Luckily, there are a number of evidence-based steps that suppliers, manufacturers and providers can take to decrease the likelihood of attacks.

For instance, suppliers of network-accessible medical devices, software and services must be compliant with current U.S. Food and Drug Administration (FDA) cybersecurity guidance documents. 
Read the article.


August 2, 2018


Topic Area: Security


Recent Posts

Achieving Better Treatment Spaces Through Co-Design
How a 20th Century industrial building became a safe space for youth seeking mental health support.


Prisma Health to Acquire 36 Urgent Care Sites in South Carolina from Novant Health
Following the close, expected November 1, 2026, the centers will operate under Prisma Health Urgent Care.


Modoc Medical Center Discloses Data Breach
Modoc reported the event to federal law enforcement and appropriate government regulators.


Creating Healthcare Campus Master Plans That Allow Movement and Respite
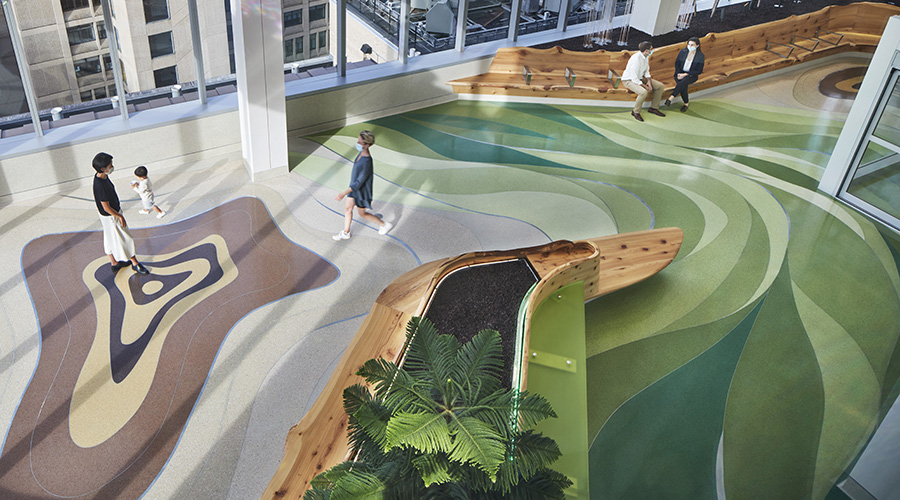
A thoughtful campus master plan looks beyond buildings to the corridors and transitional spaces that shape how people experience healthcare environments.


Aspirus Health Celebrates Opening of Chippewa Falls Hospital and Clinic

The new facility combines hospital and clinic services in one location and is designed to support patients with coordinated, patient-centered care.


FREE Newsletter Signup Form

News & Updates | Webcast Alerts
Building Technologies | & More!


All fields are required. This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.