Over 275 million medical images are currently exposed due to unsecured picture archive communication systems (PACS), according to the Department of Health and Human Services (HHS). The department alerted medical facilities to prioritize the repair of a two-year-old vulnerability. PACS are utilized for the interchange and storage of health scans and images like MRIs, CT Scans, breast imaging, and ultrasounds. The weaknesses within PACS software include known default passwords, hardcoded credentials and lack of authentication inside third party software.
HHS also stated that 130 health facilities are running systems susceptible to cyberattacks, mentioning Digital Imaging and Communications in Medicine (DICOM) issues and fundamental security lapses. Because ultrasound, CT, MRI and other radiology files are stored and exchanged on PACS servers, they rely on the DICOM formatting standard. DICOM was developed 30 years ago as the standard for the communication and management of medical imaging information and is also vulnerable to exploitation.
These security lapses and issues leave healthcare systems open to attack by hackers over the internet. This means that the vulnerable information could be easily detected and compromised by hackers from anywhere. Cybercriminals who can exploit PACS vulnerabilities could expose medical information like patient names, examination dates, images, physician names, dates of birth, procedure types, procedure locations and social security numbers," according to HC3. If a hacker got ahold of DICOM-based information that could allow for the manipulation of medical diagnoses scan falsifications, malware deployment or sabotage.
Healthcare facilities have been advised by HHS to patch their servers and review their inventory to see if they are running any PACS software. If they are, then the PACS security check should start with the validation of connections to guarantee that access is limited to authorized users only.
The HHS’s Health Sector Cybersecurity Coordination Center (HC3) suggested that systems should be configured in harmony with the documentation that accompanies them from their manufacturer. Additionally, systems and servers connected to the internet should be encrypted by enabling HTTPS.
The Medical Imaging & Technology Alliance (MITA) is also encouraging healthcare facilities to take the necessary steps to reduce their exposure to cybersecurity threats. It pointed to the manufacturer disclosure statement for medical device security (MDS2) as a starting point to establish how to ideally deploy their PACS systems in a safe and secure way. Proper healthcare data management and security is vital to protect the information of patients and providers everywhere.
 Creating Healthcare Campus Master Plans That Allow Movement and Respite
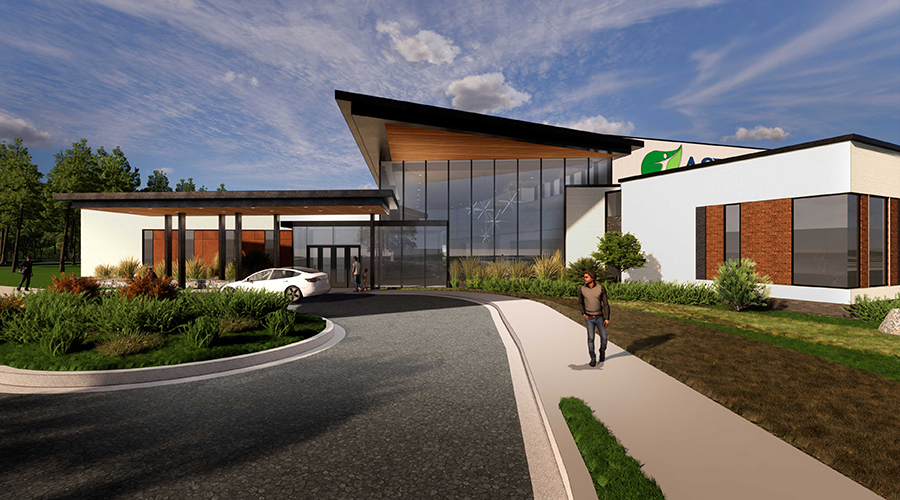 Aspirus Health Celebrates Opening of Chippewa Falls Hospital and Clinic
 AdventHealth to Open Aurora Highlands Medical Campus
 The Future of Healthcare Facility Construction Projects
 Arnprior Regional Health Upgrades Building Controls to Improve IEQ