The healthcare industry continues to fight against a consistent wave of ransomware-based cyberattacks. Although consistent, this threat of ransomware is not a new one. Between 2014 and 2020 about a third of NHS trusts were successfully attacked with ransomware, according to Open Access Government. This caused more than 200 days of downtime.
Healthcare systems have an intrinsic susceptibility to ransomware attacks due to the amount of technology within them. Technology that gives access to patient data especially is everywhere in a healthcare setting. Many systems do not implement modern software to mitigate cyberattacks. This makes it easier for those that want to take advantage of patient health records and other data in these spaces like test results. The outcomes of cyberattacks can be harmful to healthcare operations.
For example, a recent cyberattack hurt a network of hospitals and clinics in Ohio and West Virginia, according to Nextgov. This attack forced the network to temporarily cancel surgeries and divert patients with emergencies to other facilities. The system had to shut down its information technology systems as well. Since the pandemic began, cybersecurity professionals have seen an increase in attempted ransomware and hacking attacks in healthcare systems, according to The PEW Charitable Trusts.
Ransomware kits found on the dark web make it easier for cybercriminals to take advantage of weak information technology systems. These criminals disrupt backup systems, delete shadow copies and unlock files to maximise their impact. They often hold precious data and force organizations to pay large ransoms. Health systems should execute a zero trust plan to mitigate cyber attacks. This plan mandates that these spaces should not give access to any user until they prove their identity. After being given access, the user should only have access to the information they need. For example, a doctor could only have access to their own patients’ records. This limits the effects of an attack if a cybercriminal were to get ahold of access information. Access and identity restrictions should be the foundation of a security strategy based on a zero trust method.
 Elevating EVS Professionals: The Case for Certified Hygiene Specialists
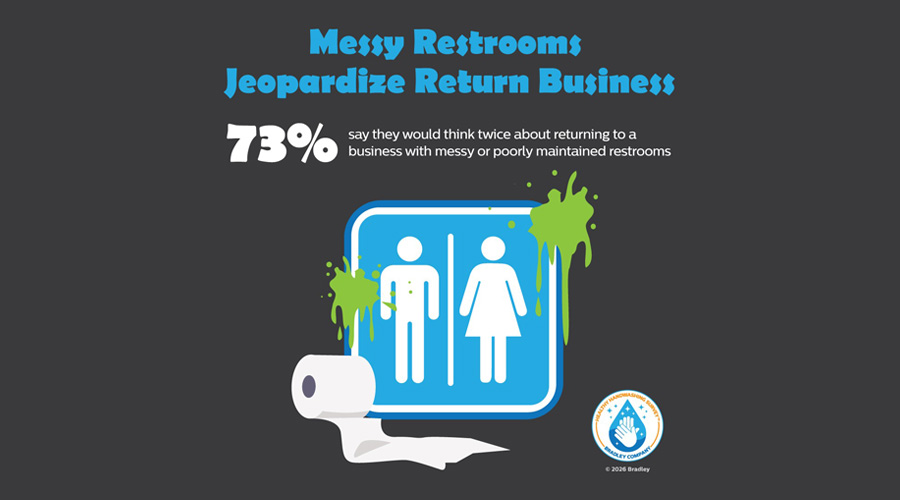 Global Handwashing Day and the Importance of Well-Maintained Restrooms
 Duke Health and CaroMont Health Partner to Develop Two New Hospitals
 Designing for the Psychology of Waiting
 UT Health Sciences Breaks Ground on College of Medicine Interdisciplinary Building