Mobile devices have created a series of problems for healthcare IT managers, from enhanced targets of cyber attacks to sources of infection. Managers looking to minimize the risk of cyber attacks involving a range of mobile devices — and in the process, better protect valuable patient information — now have guidance to help achieve those goals.
NIST recently shared draft guidance for enterprise bring-your-own-device policies to provide system administrators with a standards-based approach and need tools for the privacy and security of personally owned mobile devices accessing enterprise resources, according to Health IT Security.
The Mobile Device Security: Bring Your Own Device (BYOD) practice guide aims to support entities with managing the increasing number of devices owned by employees that remotely perform work-based activities. While the BYOD practices allow for greater flexibility to remote work, the use poses unique challenges and threats to the enterprise environment.
 Extreme Weather: The Maintenance-Resilience Link
 Encompass Health Lower Providence Opens in Pennsylvania
 Intermountain Health Acquires Fairbourne Building for Healthcare Hub and Medical Campus Conversion
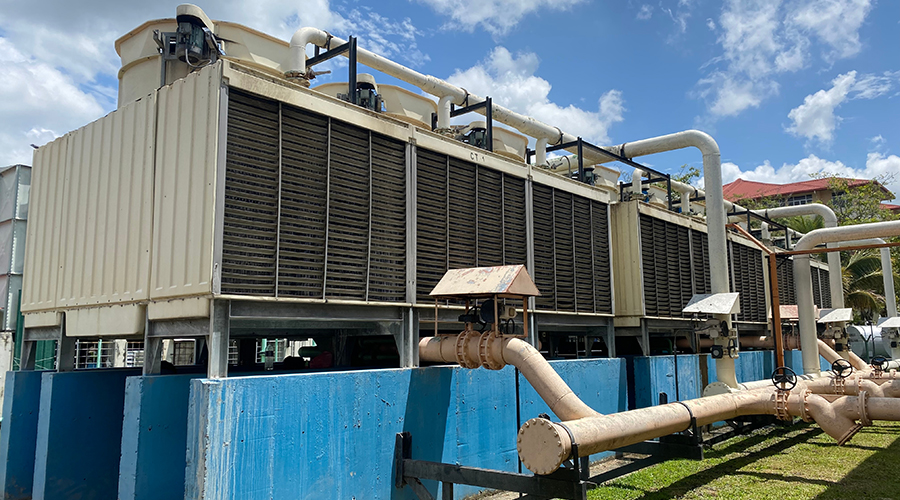 Cooling Towers at NYC Health + Hospitals/Lincoln Test Positive for Legionella
 Prefabricated Wall Panels Accelerate UCF Lake Nona Medical Center Construction