Native American Health Center (NAHC) has become aware of a data security Incident that may have resulted in an unauthorized access to sensitive personal information.
On November 19, 2023, NAHC was the victim of a cybersecurity incident. Upon discovery of this incident, NAHC immediately disconnected all access to the network and promptly engaged a specialized third-party cybersecurity firm to assist with securing the environment, as well as, to conduct a comprehensive forensic investigation to determine the nature and scope of the incident.
In January 2024, the forensic investigation found evidence to suggest that some NAHC files were accessed by an unauthorized actor. Based on the findings of the forensic investigation, NAHC began an extensive and comprehensive review of the potentially affected files and folders to identify what information was impacted. This review identified that some individuals’ information may have been impacted by this incident. On May 28, 2024, NAHC finalized the list of individuals to notify and identified their addresses to the extent available. Notice was mailed out to identified individuals on June 3, 2024.
The information impacted varied by individuals but included name, address, medical information, or Social Security number. A formal notice letter has been sent to those who have had their sensitive information impacted, and the identified the types of information involved.
Upon discovery of the Incident, NAHC moved quickly to investigate and respond to the Incident and assessed the security of its systems. Specifically, NAHC took the following steps, including but not limited to: implement a comprehensive measure to replace all hard drives in every workstation to enhance overall security; continue the use of multifactor authentications for all logins, a measure already in place prior to the breach; continue annual HIPAA privacy & security risk assessments; extend the deployment of a multifactor authentication system that will replace the use of passwords with the scan of a fingerprint of tap of a badge (currently in pilot in select departments); uphold restricted access to all IT department offices & server rooms for heightened physical activity; maintain the practice of restricted access & ongoing monitoring for buildings and sites equipped with key card access, ensuring controlled and monitored entry; and conduct ongoing annual reviews of policies, procedures, employee training programs that cover cybersecurity, HIPAA compliance & privacy, took steps and will continue to take steps to mitigate the risk of future harm.
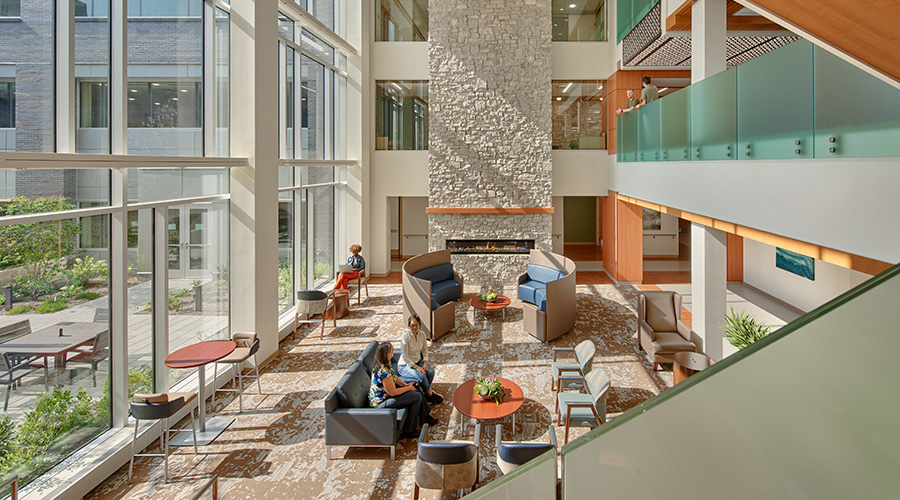 Designing for the Psychology of Waiting
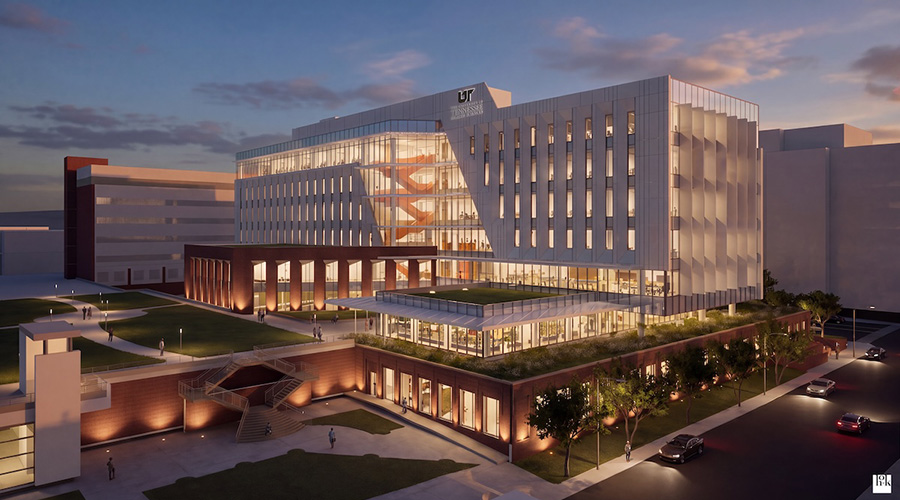 UT Health Sciences Breaks Ground on College of Medicine Interdisciplinary Building
 Vandalia Health, Mary Free Bed Break Ground on New Rehabilitation Hospital
 Why New Era of Care Demands an Ambulatory Facilities Approach
 ClearSky Health Plans New Medical Rehabilitation Hospital in North Carolina