WindRose Health Network recently learned about a security incident that involved its computer network. The incident involved a previously undisclosed vulnerability in a remote-management tool that is used by one of its vendors. This remote-management tool can be used to access some of WindRose’s systems. Upon learning of the incident, it promptly began working with its vendor and cybersecurity experts to investigate. WindRose is providing this notice to share information about what happened and what it is doing in response.
On August 4, 2026, it was informed by one of its vendors about a previously undisclosed vulnerability in the remote-management tool it maintains and uses to access its network. WindRose immediately took steps to secure its environment and began working with cybersecurity experts to assist in the investigation. Based on the investigation, it believes that an unauthorized third party used this vulnerability to gain access to one of its servers from August 3 to August 4, 2026. This incident did not have any impact on the systems that host our electronic medical records.
The investigation determined that the following types of information were present in some of the affected files: patient names, patient identification numbers, health insurance information, dates of service and the names of the medical providers.
WindRose hired third-party experts to help it perform an investigation into the unauthorized activity and further secure its systems and the information it maintains.
 Building Around Care: Lessons in Modernizing Active Healthcare Environments
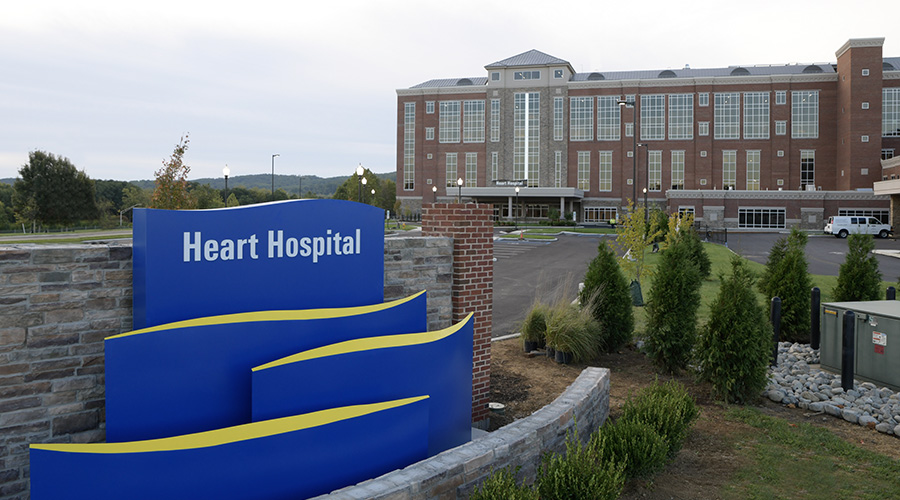 St. Luke's Heart Hospital Opens at Anderson Campus in Pennsylvania
 How Efficiency Checklists Help Hospitals Save Energy, Water and Money
 Intermountain Healthcare Receives $50M Gift for Standalone Children's Hospital